POPI Act Website Compliance and the Rules for Personal Data

POPIA reaches beyond online shops: it applies to public and private organisations that process personal information about individuals in South Africa, regardless of industry. South Africa’s Protection of Personal Information Act is Act 4 of 2013. That makes popi act compliance for websites relevant whenever a site collects or uses personal information, including through enquiry forms, mailing lists or online identifiers.

A privacy notice is important, but it is only one part of website compliance. POPIA also affects how a site collects, uses, stores and protects personal information, including how it presents consent choices and handles requests from people.

This guide explains who POPIA applies to, what counts as personal information and what an Information Officer does. It also covers practical website considerations, from consent on forms to clear privacy information, so you can identify steps to align your site’s data practices with the Act.

Key Takeaways

  • Recognise the personal information a website may collect, including through forms, cookies and online identifiers.
  • Understand how data subject rights shape the way your organisation handles access, correction and removal requests.
  • Clarify the Information Officer’s role in guiding privacy practices and supporting compliance responsibilities.
  • See how POPIA’s scope and penalties make responsible data handling relevant to organisations of different sizes.
  • Explore how clear consent choices, privacy notices and thoughtful website design can support stronger data practices.

What counts as personal information under POPIA?

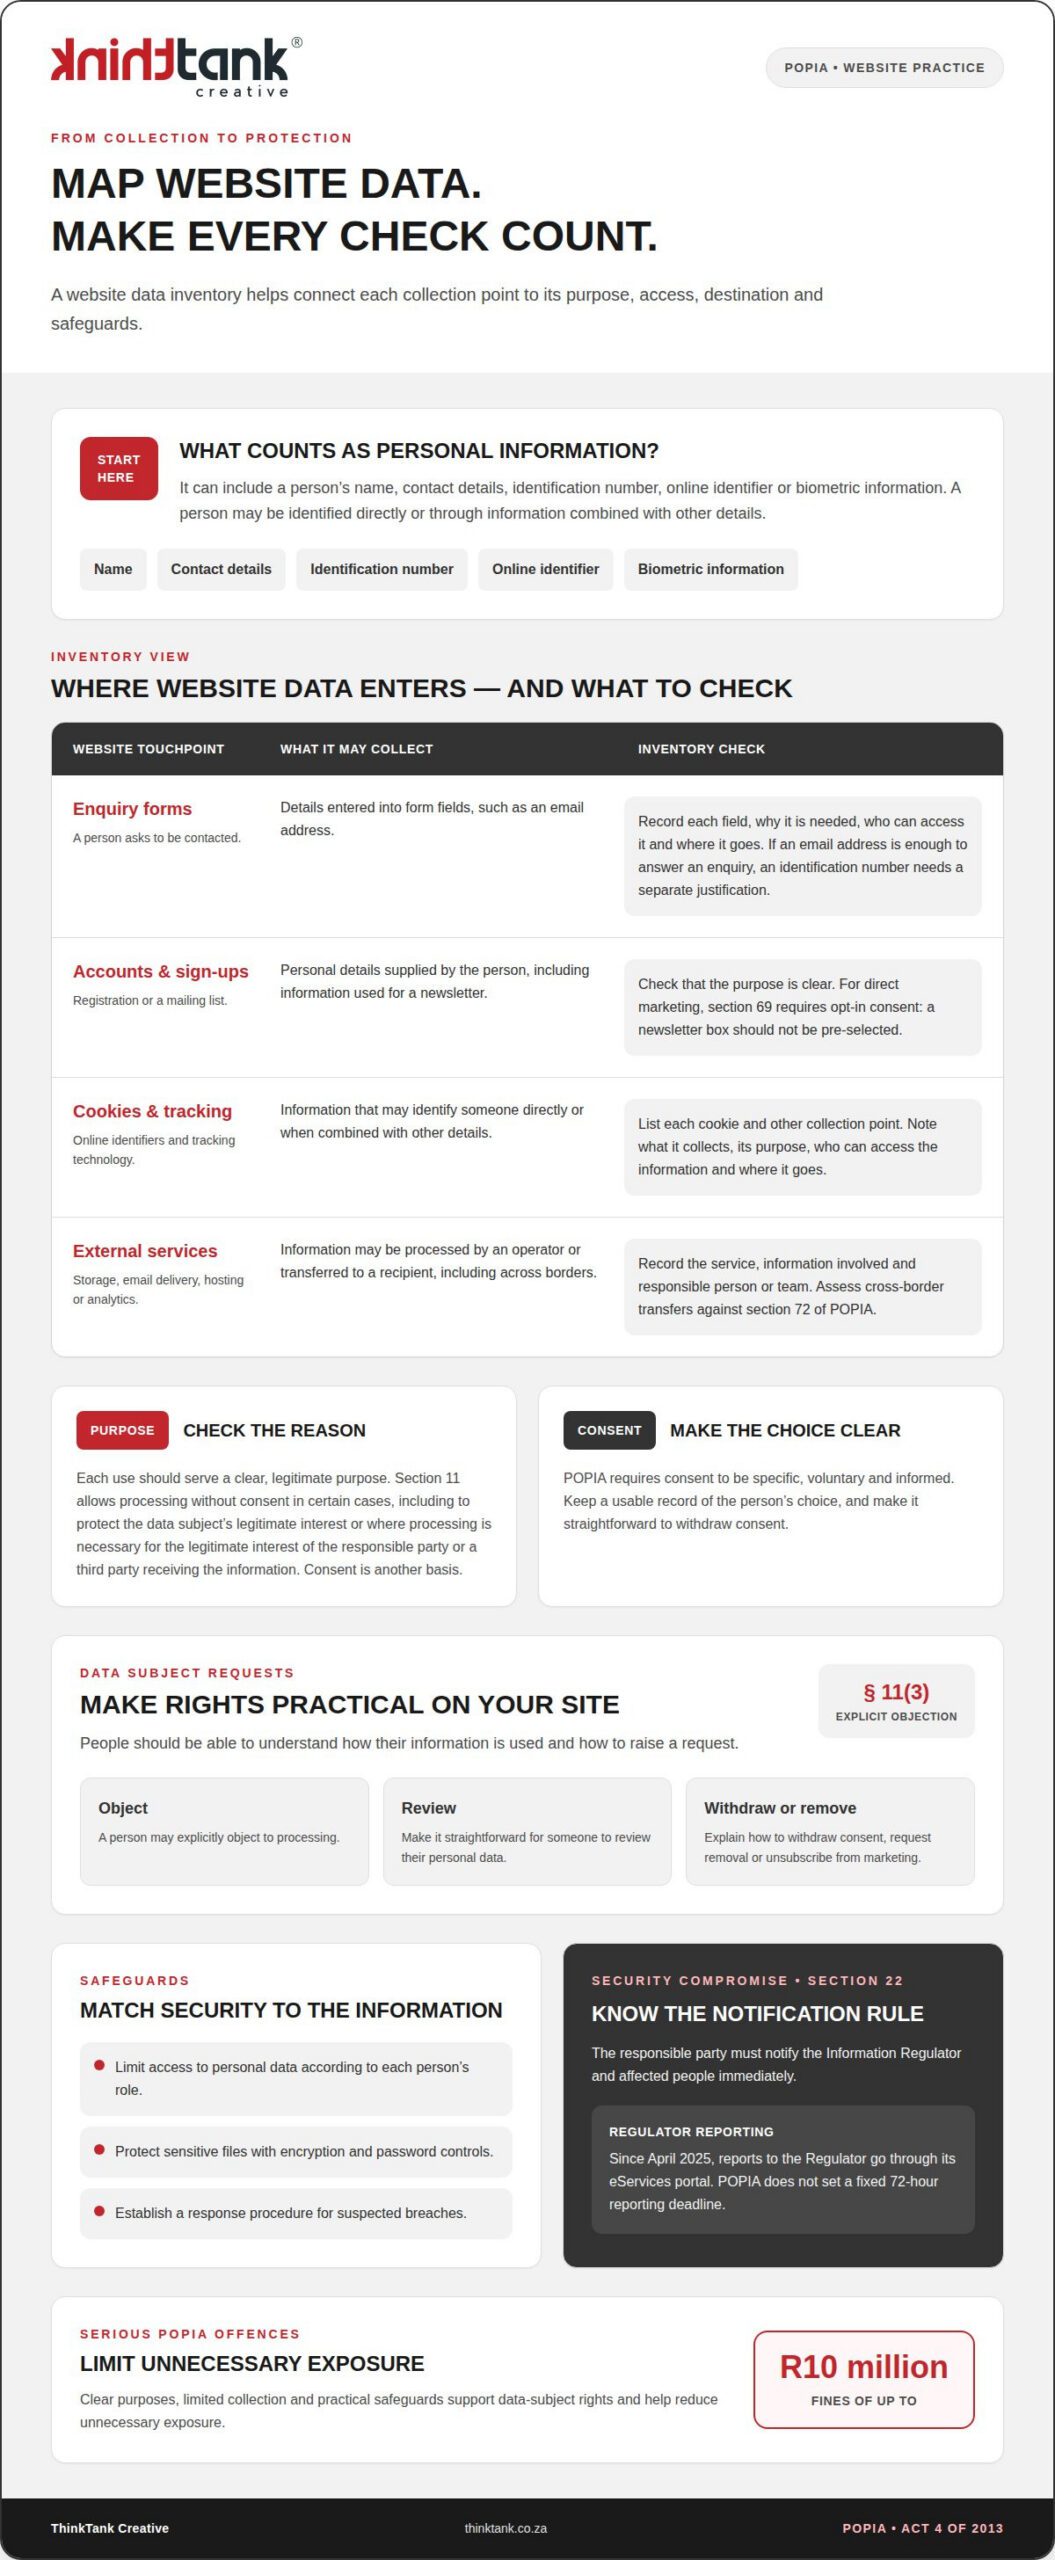
Under South Africa’s Protection of Personal Information Act, personal information can include a person’s name, contact details, identification number, online identifier or biometric information. A website may collect it through an enquiry form, account registration, newsletter sign-up or tracking technology. Information can identify someone directly or when combined with other details.

Start with a data inventory. List every form field, cookie and other collection point, noting what information it collects, why, who can access it and where it goes. Then check whether each use serves a clear, legitimate purpose. If a contact form needs only an email address to answer an enquiry, collecting an identification number requires a separate justification.

Section 11 of POPIA allows processing without consent in certain cases, including where it protects the data subject’s legitimate interest or is necessary for the legitimate interest of the responsible party or a third party receiving the information. Consent is another basis, and POPIA requires it to be specific, voluntary and informed. Section 69 requires opt-in consent for direct marketing, so a newsletter box should not be pre-selected.

Data subjects have a role in how their information is processed. Under section 11(3), a person may explicitly object to processing. A website should also make it straightforward for someone to withdraw consent, review their personal data or request its removal. A privacy policy should explain what information is collected, why it is used and how people can raise a request or unsubscribe from marketing.

Security needs to match the information held. Limit access to personal data according to each person’s role, protect sensitive files with encryption and password controls, and establish a response procedure for suspected breaches. Section 22 concerns security-compromise notification. The responsible party must notify the Information Regulator and affected people immediately; since April 2025, reports to the Regulator go through its eServices portal. POPIA does not set a fixed 72-hour reporting deadline.

Keep the inventory and privacy notice aligned as website forms, analytics tools and marketing practices change. If a data breach exposes an email list, for example, the response procedure should identify the affected information, restrict access and guide the required notifications. Serious POPIA offences may result in fines of up to R10 million. Clear purposes, limited collection and practical safeguards help reduce unnecessary exposure while supporting data-subject rights.

Information Officer registration and responsibilities

Every company in South Africa is legally required to appoint an Information Officer. Businesses should register the officer with the Information Regulator, which monitors and enforces POPIA. The role links an organisation’s personal-information practices with its compliance responsibilities. For a website, this means understanding how enquiry forms, mailing lists and analytics tools collect or use information.

Make the Information Officer’s responsibilities practical. The officer can coordinate processes for privacy queries, help staff understand how information is handled and support responses to data-subject requests. Map each website collection point to the person or team responsible. For example, record who manages newsletter subscriptions and who handles requests to withdraw consent.

Clear terminology helps define those responsibilities. A data subject is the person whose personal information is processed. The responsible party determines why and how that information is processed, whilst an operator processes it for the responsible party. If an online form sends details to an external service for storage or email delivery, the Information Officer should record that relationship and the information involved.

Cross-border transfers need particular attention. Section 72 of POPIA sets out conditions for transferring personal information across borders. A website may involve an overseas hosting or analytics provider, so the Information Officer’s assessment should identify where information goes and which recipient handles it. The transfer must be considered against section 72, rather than assumed acceptable simply because the service supports the website.

Consent records also need to be understandable and usable. Consent requests should clearly explain the processing and let people make an informed choice. The Information Officer can help ensure that a consent request identifies the relevant processing and records the person’s choice. For instance, a marketing sign-up should distinguish an affirmative opt-in from a pre-selected box, while preserving a record of the choice made.

Registration is only one part of the role. The Information Officer also needs a working understanding of how website information moves through the organisation, from collection to access, sharing and removal. A processing register can link each form or tool to its purpose, internal owner, operator and any cross-border transfer. This helps route requests to the right team and explain the organisation’s practices consistently.

As website features change, update the Information Officer’s records too. Adding a booking form, CRM integration or overseas email platform can change who receives information and how it is used. Recording such changes helps the officer coordinate consent processes, review responsibilities and keep POPIA practices aligned with the site’s actual operation.

What is POPIA compliance?

POPIA compliance means handling personal information lawfully, with safeguards that match its use. South Africa’s Protection of Personal Information Act is Act 4 of 2013. For a website, this can mean documenting why an enquiry form collects an email address, who can access submissions and how long they are retained. A privacy notice alone cannot show whether those practices are correct.

The Information Regulator monitors and enforces compliance by public and private bodies. An organisation should be able to explain its website practices with records, not just policy statements. For example, document what a mailing-list form collects, why it collects it and how consent is recorded. Assigning the Information Officer to coordinate these records creates a practical point of accountability.

Non-compliance can carry serious consequences. Serious offences under POPIA may result in fines of up to R10 million. That figure is a maximum, not an automatic charge for every website error. The nature of the conduct matters: an organisation should distinguish an isolated process gap from practices that disregard lawful handling of personal information.

Criminal penalties can also include imprisonment. Individuals responsible for serious POPIA violations may face imprisonment for up to 10 years, while less serious offences may carry imprisonment of up to 12 months. These are distinct maximum periods, not a prediction of the outcome in a particular case. They underline why clear responsibilities and documented measures matter.

Civil proceedings are another consideration if personal information is mishandled. Preserve relevant records, such as the privacy notice in force, form wording and consent logs. If a dispute concerns an online marketing sign-up, these records can help establish what the person was told and what choice they made. Once a complaint arises, avoid changing or deleting relevant material.

Build compliance into routine decisions. Before adding a website feature, record its purpose, the information it uses and the people or systems that can access it. When a form changes, update the privacy information and internal records together. The Information Officer can coordinate these steps, while responsible teams ensure the published wording reflects how the site actually works.

A proportionate response starts by identifying and addressing the cause of a gap. If a subscription form obscures its marketing purpose, make the choice clear and retain evidence of the revised process. Consider whether the correction also affects existing records or connected systems. Consistent documentation helps an organisation explain its decisions to the Information Regulator and respond coherently if concerns escalate.
POPI Act Website Compliance and the Rules for Personal Data

POPI: Why is Website Compliance Important?

POPIA’s scope depends on the processing of personal information, not an organisation’s size or industry. A website may process information when it collects or uses details about people in South Africa, making popi act compliance for websites relevant to organisations with an online presence.

Compliance for small businesses

For a small business, popi act compliance for websites means considering how online forms, mailing lists and other features handle personal information. A sole trader’s contact form raises the same kinds of data-handling questions as a larger company’s website. Identify what each feature collects, why it is needed and who is responsible. This gives small teams a practical starting point without tying compliance to business size.

POPIA applies to public and private organisations processing personal information about individuals in South Africa, regardless of industry. A community organisation collecting membership details online and a company receiving sales enquiries both need to consider the Act. The Information Regulator monitors and enforces compliance by public and private bodies. The relevant factor is the processing of personal information, not workforce size or public profile.

Websites collect information directly through forms, account registration and mailing-list subscriptions. They may also process online identifiers through analytics or advertising tools. Define a purpose for each feature and explain it clearly to the data subject. For example, an enquiry form can explain why it requests contact details, while a separate marketing sign-up makes its purpose clear before submission.

POPIA and GDPR applicability

POPIA applies to processing personal information about individuals in South Africa. The GDPR may also apply to a South African business processing the personal data of EU consumers. This distinction matters for websites serving audiences in both markets. Consider whose information the organisation processes and where those individuals are, rather than relying only on the organisation’s location.

The GDPR and POPIA are separate laws, so meeting one does not automatically resolve obligations under the other. The GDPR’s maximum fine can be 4% of global annual turnover; this is not a POPIA penalty. For a South African website addressing EU consumers, assess the audience, information collected and activities involving that information to determine which law may apply to each processing activity.

Website features and audiences can change. Adding an online shop, analytics tool or international marketing campaign may affect whose information is processed and where it goes. Record each significant update, its purpose and its relevant audience. This helps an organisation reassess POPIA’s scope and whether GDPR considerations arise, rather than assuming every feature has the same compliance impact.

Website compliance solutions

Build privacy choices into the points where visitors interact with your website. Forms, cookie notices and mailing-list sign-ups should explain the relevant processing of personal information. Effective popi act compliance for websites starts with consent that is specific, voluntary and informed. A pre-ticked box does not demonstrate an active choice, so use an empty box or another clear opt-in action.

Connect each form field to a clear purpose. An enquiry form might request a name and email address to respond, while a separate, optional choice covers marketing messages. Explain what happens after submission and provide a simple way to withdraw consent. For direct marketing, section 69 requires opt-in consent. Keep a record of each choice and let recipients unsubscribe from future messages.

Cookie notices should clearly describe the site’s cookie use and obtain explicit consent. Do not present acceptance as the only practical route. A visitor who declines optional tracking has not agreed to it. Review each analytics or advertising tool, including the information it collects and the parties that receive it. A banner is useful only if the site behaves in line with the visitor’s choice.

Give people a practical way to exercise their data-subject rights. A privacy notice should explain how individuals can request access to personal information, ask for correction or seek removal. Provide a suitable contact channel and explain what details are needed to locate a record. Internally, route requests to the responsible team and track progress rather than leaving them in a general inbox.

Technical safeguards should support those commitments. Limit access to personal information by role, protect sensitive files with encryption and password controls, and remove access when staff responsibilities change. Keep a record of website systems that handle submissions, such as a form database or email platform. This gives the Information Officer a clearer view of the systems involved if a suspected breach occurs.

Review the site whenever its features change. Before adding a booking tool, advertising pixel or sign-up field, assess its purpose, collection points and recipients. Then update the privacy notice, consent wording and internal records together. This keeps explanations aligned with actual data processing and makes ongoing popi act compliance for websites part of the change process, not a late addition.

For a redesign or technical update, align the interface and data choices from the outset. Plan a website design and development project around clear forms, accessible privacy information and deliberate consent choices, so these elements work together.

ThinkTank Creative

ThinkTank Creative designs and develops websites that present privacy information and data choices clearly. If you’re planning a new site or revising forms, the team’s Website Design and Development and creative design services can support a considered user experience. Bring consent options, privacy notices and enquiry journeys into the design process, while your organisation remains responsible for its POPIA obligations and personal-information decisions.

Consider this support when website changes affect how visitors submit information or make choices. A coherent design can make these interactions easier to understand and use. Contact ThinkTank Creative to discuss your website and its privacy-related design needs.

Build privacy into your next digital step

Treat privacy as part of the experience you create for every visitor, not text added after a website goes live. A thoughtful approach to popi act compliance for websites connects clear information, meaningful choices and a consistent user journey. As your site and digital communications evolve, revisit how each interaction feels to visitors and how it supports your organisation’s data practices.

ThinkTank Creative can shape your digital experience through website design and development, creative design and social media marketing. These services support how your organisation presents itself online, while compliance decisions remain grounded in your responsibilities under POPIA.

Start a conversation about the next stage of your online presence. Contact ThinkTank Creative to discuss your goals and explore a considered way forward. Clearer digital experiences begin with deliberate choices, and each thoughtful improvement can strengthen the relationship between your organisation and its audience.

Frequently Asked Questions

What is POPIA and who does it apply to?

POPIA is South Africa’s Protection of Personal Information Act, Act 4 of 2013. It applies to public and private organisations processing personal information about people in South Africa, regardless of industry or business size. For example, a community organisation collecting membership details online may need to consider the Act, just like a retailer receiving customer enquiries. The individual whose information is processed is known as the data subject.

What is the penalty for non-compliance?

Serious POPIA offences may result in fines of up to R10 million, and individuals responsible for serious violations may face imprisonment for up to 10 years. Less serious offences may carry imprisonment for up to 12 months. These are maximum penalties, not automatic outcomes for every compliance failure. The nature of the conduct matters, so a neglected marketing preference and deliberate misuse of personal information are not interchangeable situations.

Does POPIA require cookie consent?

Websites should clearly explain cookie use and obtain explicit consent, particularly when cookies support tracking or advertising. A banner should let visitors make an active choice rather than rely on a pre-ticked box. For example, someone selecting “No” should not be treated as having agreed to optional tracking. The notice and the site’s actual behaviour should match, so the choice has practical effect.

What are consumer rights under POPIA?

People whose information is processed can object to processing under section 11(3) and withdraw consent. They should have a clear way to unsubscribe from marketing and to review or request removal of personal information. For example, a person who no longer wants promotional emails should be able to use an unsubscribe route. Organisations should explain how to raise requests and ensure they reach the team responsible for handling them.

What are the benefits of being compliant?

Compliance gives an organisation a clearer framework for handling personal information and responding to people’s choices. For example, keeping a record of newsletter preferences can help prevent messages being sent after someone unsubscribes. Clear explanations also help visitors understand why a form asks for particular details. These practices support consistent interactions and give the organisation a stronger basis for explaining how its website uses information.

What are the exceptions to the POPIA Act?

Section 11 allows certain processing without consent, including where processing protects a data subject’s legitimate interest or is necessary for the legitimate interest of the responsible party or a recipient. This is a basis for processing, not a general exemption from POPIA. The purpose and circumstances matter. A business should not assume that a legitimate-interest rationale removes the need to explain its processing or respect a person’s explicit objection.

What is an Information Officer and is one required?

An Information Officer is appointed to support an organisation’s POPIA responsibilities. Every company in South Africa is legally required to appoint one, and businesses should register the officer with the Information Regulator. For example, the officer can coordinate who handles website privacy enquiries and how requests reach the appropriate team. Registration provides a formal point of accountability, but relevant staff still need to follow the organisation’s processes.

What does POPIA require from websites in South Africa?

A website should explain its personal-information practices, make consent choices clear and handle information securely. For example, an enquiry form can state why it requests contact details, while a separate, unselected option invites visitors to sign up for marketing. Sites should also provide a way for people to exercise their choices and unsubscribe. Appropriate measures depend on the information collected, the site’s purposes and its connected tools.
PAIA Manual for Website South Africa: The 2026 Compliance Guide

What if your beautifully designed digital presence is actually a legal liability waiting to be flagged by the Information Regulator? While you focus on growth and user engagement, the requirement for a compliant paia manual for website south africa has evolved from a back-office task into a critical pillar of digital trust. We understand that the overlapping demands of POPIA and PAIA often feel like a complex maze of terminology and technical hurdles. It's completely natural to feel overwhelmed by the prospect of integrating rigid legal mandates into a fluid, creative web design.

This guide promises to transform that confusion into clarity, providing you with the exact framework needed to achieve total compliance in 2026. You'll discover how to master the latest regulatory standards whilst ensuring your legal documents are seamlessly integrated into your site’s architecture. We'll explore the essential components of the updated template, the registration of Information Officers, and our signature methodology for embedding these requirements into a high-performance website that protects your brand and your peace of mind. By the end of this article, you'll have a clear roadmap to navigate these complexities with quiet assurance and strategic precision.

Key Takeaways

  • Understand why a compliant paia manual for website south africa is a non-negotiable legal requirement for transparency and corporate accountability in 2026.
  • Learn to harmonise your PAIA manual with POPIA protocols to ensure your digital presence addresses both information access and data protection effectively.
  • Identify the essential statutory fields and Information Officer details required to satisfy the latest Information Regulator templates and mitigate the risk of enforcement action.
  • Gain a methodical framework for drafting and publishing your manual, ensuring it remains a functional and accurate reflection of your business records.
  • Discover how a structured 5-stage development process seamlessly integrates complex legal requirements into your website design whilst maintaining a premium brand identity.

What is a PAIA Manual and Why is it Mandatory for Your Website?

Transparency is the bedrock of a modern, democratic economy. The Promotion of Access to Information Act (PAIA) serves as the legislative engine that drives this principle, ensuring that information is accessible to those who need it to protect their rights. It isn't just a legal hurdle; it's a commitment to corporate accountability that resonates with your audience. By providing a clear path for information requests, you're signaling that your business operates with integrity and openness.

Your PAIA manual is the instructional guide for this process. It outlines the categories of records your business maintains and the specific steps a requester must take to view them. For any modern enterprise, a paia manual for website south africa is a vital digital asset. Because your website is your most visible storefront, the law requires that this manual be easily accessible to any visitor. This accessibility ensures that your business remains transparent whilst providing a clear roadmap for legitimate information requests.

To better understand how this framework functions in a corporate environment, watch this helpful video:

We view compliance as a synergistic effort. PAIA works amongst POPIA regulations to create a comprehensive data management strategy. Whilst POPIA focuses on the protection and ethical processing of personal data, PAIA ensures that the right to information remains unhindered. This balance is crucial for maintaining the integrity of your digital operations. It's about creating a culture of accountability that resonates with your clients and stakeholders alike.

The Legal Necessity for South African Private Bodies

Section 51 mandates that every private body must compile and maintain this document. A private body is officially defined as any natural person who carries on a trade, profession, or business, as well as any partnership or juristic person. The Information Regulator has shifted toward a more proactive enforcement model in 2026. They now actively monitor digital platforms to ensure that manuals are updated and reflect the latest statutory requirements. It's no longer enough to have a static document; it must be a living reflection of your current record-keeping practices.

Consequences of Non-Compliance in 2026

The cost of neglecting these requirements extends far beyond mere paperwork. Administrative fines can be substantial, but the damage to your brand’s reputation is often more difficult to repair. A missing or outdated manual signals a lack of professional rigour, which can directly stall your lead generation strategies for South African businesses. High-value clients seek partners who demonstrate meticulous attention to detail and legal compliance. Without professional oversight, you risk leaving your business vulnerable to both regulatory scrutiny and a loss of market trust.

PAIA vs POPIA: Understanding the Compliance Synergy

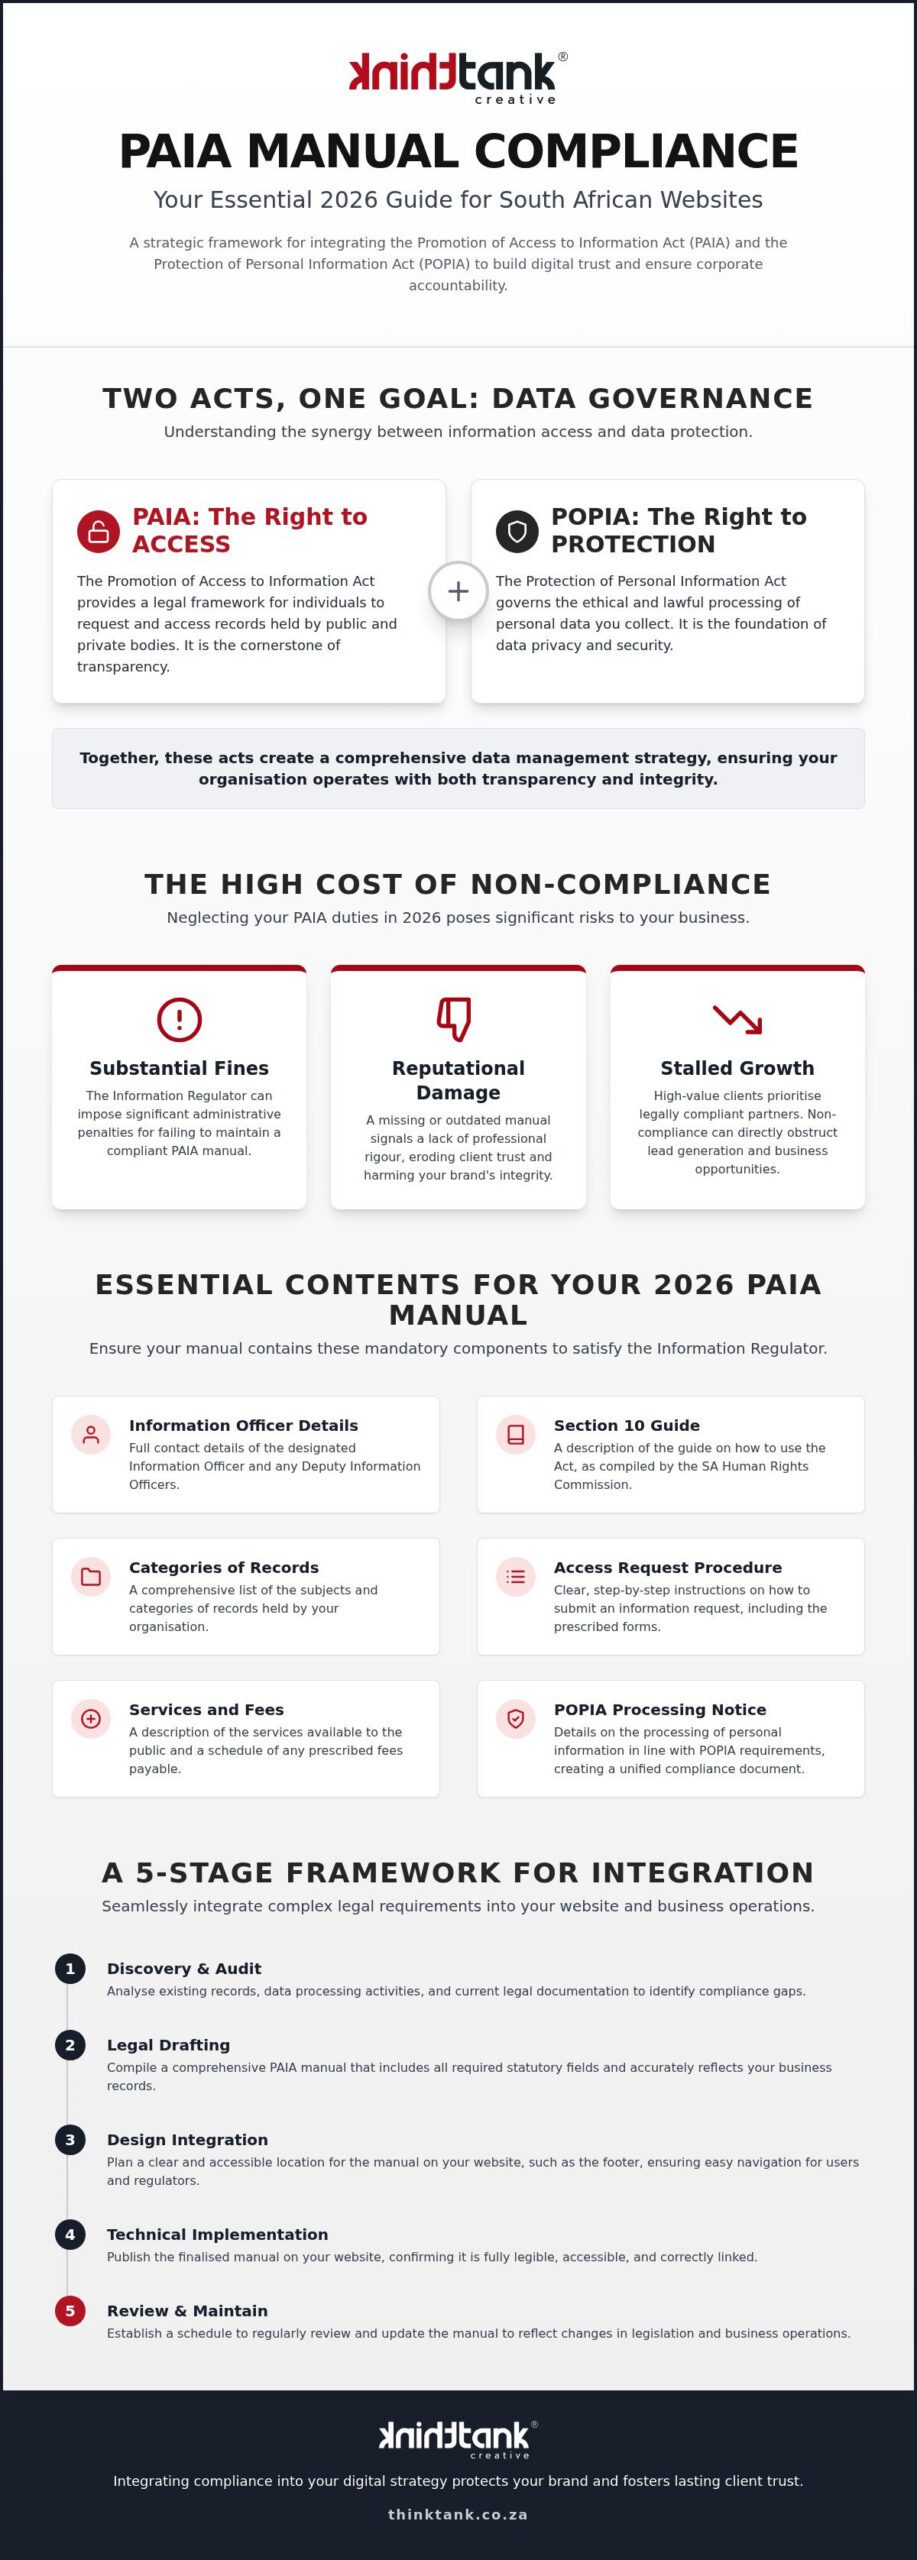
Achieving digital compliance requires a nuanced understanding of how different legislative frameworks intersect to protect both the business and the consumer. Whilst many organisations treat them as separate silos, PAIA and POPIA are actually two sides of the same transparency coin. POPIA, the Protection of Personal Information Act, focuses on the protection and ethical handling of data you collect. In contrast, PAIA is about access, providing a legal mechanism for individuals to request records held by your body. Implementing a paia manual for website south africa is the necessary counterpart to your privacy policy, ensuring you address both the right to privacy and the right to information.

Your website must present these documents with absolute clarity. A common mistake is burying legal links in obscure corners, which can frustrate users and signal a lack of transparency to regulators. We recommend organising these protocols within your site's footer, grouped logically under a "Legal" or "Compliance" heading. This structure allows the Information Officer to manage requests efficiently through a dedicated interface, bridging the gap between statutory requirements and user experience. Following the Information Regulator's PAIA guidelines ensures that your "Access" protocols are as robust as your "Protection" ones.

The Dual Mandate of the Information Regulator

The Information Regulator oversees both Acts through a unified eServices portal, streamlining the administrative burden for businesses. You must register your Information Officer on this portal before your manual is officially published. This registration is a prerequisite for submitting annual reports and ensures your organisation is recognised as a compliant entity. By centralising these functions, the Regulator makes it easier to facilitate the "Right to Access" seamlessly, provided your website is built to support these digital interactions. It's a methodical process that rewards thoroughness and strategic planning.

Integrating Compliance into Custom Website Design

Legal documentation should never feel like an afterthought. High-quality custom website design South Africa must account for statutory requirements from the initial wireframing stage. We avoid the "tacked-on" look by ensuring your PAIA manual and privacy pages reflect your brand's visual identity and tone. This integration turns a dry legal necessity into a seamless part of the brand journey, reinforcing trust at every touchpoint. Mobile-first accessibility is equally critical; your legal downloads must be as easy to read on a smartphone as they are on a desktop. If you're looking to refine your digital footprint, our team is ready to assist with website maintenance and support to keep your legal pages current and functional.

What Must Your 2026 PAIA Manual Contain?

Precision is the hallmark of a compliant PAIA manual. It's not merely a list of contact details; it's a comprehensive map of your organisation's data infrastructure. To ensure your paia manual for website south africa meets the 2026 standards, it must clearly identify the Information Officer and the head of the private body. This section acts as the primary point of contact for the Information Regulator and any person seeking access to records. Additionally, the manual must include a reference to the Regulator's official guide on how to use the Act, providing a clear pathway for citizens to exercise their constitutional rights.

A robust manual details every subject on which the body holds records, ranging from internal corporate governance to external client interactions. This categorisation is essential because it informs the public about what is actually available for request. You must also outline the exact procedure for making a request, including the submission of Form 2 and the payment of prescribed fees. This level of detail transforms the document from a static requirement into a functional tool for transparency. It ensures that your business remains beyond reproach whilst facilitating legitimate requests for information.

Standard Categories of Records for SA Businesses

Modern businesses generate vast amounts of data, and your manual should reflect this digital reality. Standard categories typically include financial records, human resources documentation, and operational data. However, a digital-first approach requires you to account for website-specific records, such as user logs and digital transaction histories. Clearly distinguish between records that are automatically available, such as your public-facing marketing materials, and those that require a formal request. This distinction reduces unnecessary administrative work for your team whilst ensuring you remain fully compliant with the law.

Prescribed Forms and Fee Structures

Efficiency in compliance is driven by accessible documentation. Your website should host a downloadable version of Form 2, the official Request for Access to Record, to facilitate a smooth user experience. Transparency regarding fee structures is equally important. Whilst you cannot waive the statutory request and access fees, presenting them clearly within your manual demonstrates professional integrity. Ensure your manual is updated annually to reflect the current fee schedules in ZAR as determined by the Information Regulator. This meticulous approach ensures your business is never caught off guard by regulatory shifts or outdated documentation.

PAIA Manual for Website South Africa: The 2026 Compliance Guide

Publishing Your Manual: A Step-by-Step Implementation Guide

Executing the publication of a paia manual for website south africa requires a blend of legal precision and technical foresight. Start by drafting the document using the latest Information Regulator templates, ensuring every statutory field is populated with exactitude. A meticulous review phase follows, where you validate the content against 2026 regulations to ensure no recent legislative shifts have been overlooked. This isn't just about compliance; it's about building a foundation of trust with your digital audience through transparent record-keeping practices.

Once finalised, the manual should be integrated into your site as a searchable PDF or a dedicated HTML page. We recommend placing the link strategically within your footer, ensuring it doesn't get lost amongst other common website design mistakes to avoid. A clear, accessible link demonstrates that you value transparency and take your regulatory obligations seriously. This placement also ensures that the document is easily reachable from any page on your site, satisfying the Regulator's requirement for permanent accessibility.

Technical Hosting Requirements

Visibility is paramount for statutory documents. Optimise your PDF file names using descriptive, keyword-rich titles to enhance search engine visibility and accessibility for screen readers. You must ensure the manual is indexed by Google so that it's discoverable by the public, whilst maintaining robust security protocols to protect your server from malicious bots. We emphasise the importance of persistent URLs. A broken link in the Regulator's records can trigger a compliance audit, so your file structure must remain stable during any site updates or migrations. This stability reflects the reliability of your brand's digital infrastructure.

The Information Officer Registration Process

Registration is the final hurdle before your manual goes live. Use the Regulator’s eServices portal to register your Information Officer, a process that requires specific corporate details and a commitment to data stewardship. Once registered, link the resulting Information Officer's certificate to your internal digital compliance folder for easy retrieval during inspections. This requires constant communication between your web development team and your legal officer to ensure the public-facing manual matches the Regulator's database exactly. If you find the technical heavy lifting daunting, our team can streamline the process through expert website design and development tailored to South African standards.

Aligning your digital presence with national regulations shouldn't come at the expense of your brand's aesthetic or functional excellence. At ThinkTank Creative, we treat the implementation of a paia manual for website south africa as a core component of your site’s architecture rather than a secondary addition. Since our founding in 2001, we've refined an end-to-end 5-stage development process that ensures compliance is woven into the Planning phase from day one. This proactive methodology allows us to anticipate regulatory requirements whilst honouring the creative vision that makes your brand unique. We believe that technical precision and creative design should exist in perfect synergy.

Our award-winning design team works in close collaboration with our technical developers to ensure that your legal documentation is presented with the same bespoke craftsmanship as your primary landing pages. We adopt a "We Do It All So You Don’t Have To" approach, handling the technical heavy lifting of document hosting, SEO optimisation, and secure file management. This allows you to focus on your core business objectives whilst we ensure your digital assets remain stable and compliant. Our commitment extends beyond the initial launch; we provide ongoing website maintenance and support to ensure your manual stays updated as South African laws continue to evolve.

Beyond Compliance: Building Trust Through Transparency

A well-organised PAIA manual is a powerful signal of corporate maturity. It tells your customers and partners that you are a reliable, "smart" organisation that respects the constitutional right to information. When you integrate these protocols into a broader website launch marketing plan, you're not just checking a box; you're elevating your brand's reputation. Moving from "good marketing" to "great marketing" requires prioritising user rights and data transparency. By making your compliance documents easy to find and simple to navigate, you foster a culture of trust that differentiates you from competitors who treat legal mandates as an afterthought.

Getting Started with ThinkTank Creative

Your journey toward a fully compliant and high-performing digital presence begins with a strategic conversation. We invite you to contact our team for a comprehensive audit of your current statutory documents and website structure. Whether you're launching a new venture or refreshing an established brand, we can provide an estimated cost for a compliance-first website redesign that meets the rigorous standards of 2026. We lead with expertise and follow with meticulous execution, guiding you from the initial imagination phase to a secure, legally protected digital storefront. Let's work together to transform your regulatory obligations into a strategic advantage for your business growth.

Elevate Your Digital Integrity for 2026

Mastering your regulatory obligations is far more than a simple legal checkbox; it's a strategic investment in your brand's long-term digital integrity. By harmonising the access requirements of PAIA with the protection protocols of POPIA, you create a robust ecosystem that respects user rights whilst shielding your business from enforcement risks. Compliance builds trust. This synergy ensures your digital storefront remains both welcoming to users and resilient against regulatory scrutiny.

Ensuring you have a meticulously drafted paia manual for website south africa is the definitive step toward achieving total peace of mind. Established in 2001, our expert all-rounder team utilises a comprehensive 5-stage development process to integrate these complex statutory requirements into your web architecture with absolute precision. We handle the technical heavy lifting so you can focus on scaling your vision. Secure your digital compliance with ThinkTank Creative today and transform your mandatory legal obligations into a powerful foundation for growth. We're ready to build a more transparent digital future alongside you.

Frequently Asked Questions

Is a PAIA manual mandatory for small businesses in South Africa in 2026?

Yes, a PAIA manual is mandatory for almost all private bodies in 2026, including small businesses and sole proprietors. The previous exemptions for smaller entities lapsed on 31 December 2021; this means that regardless of your turnover or staff count, you must maintain this document. Having a paia manual for website south africa ensures your business remains compliant with Section 51 of the Act whilst promoting constitutional transparency and accountability.

What is the difference between a PAIA manual and a POPIA privacy policy?

PAIA focuses on the right of access to information, whereas POPIA governs the protection and ethical processing of personal data. Your privacy policy explains how you collect and use data, whilst the PAIA manual provides the roadmap for individuals to request records held by your organisation. Both are essential components of a compliant digital presence, working in synergy to ensure you meet the dual mandate of the Information Regulator effectively.

How often should I update my website's PAIA manual?

You should review and update your manual at least once a year or whenever significant changes occur within your business structure. This includes changes to your Information Officer’s contact details, new categories of records, or updates to the prescribed fee structures set by the Regulator. Regular maintenance ensures your manual remains an accurate reflection of your organisation, preventing administrative delays when formal information requests are submitted by the public or regulatory bodies.

Where is the best place to link my PAIA manual on my website?

The most effective location is within your website's footer, grouped clearly with other legal documents like your terms and conditions. This ensures the link is accessible from every page on your site, satisfying the Regulator's requirement for permanent availability. Avoid burying it in sub-menus; a transparent approach makes your brand look more professional and reliable to both customers and regulatory inspectors who monitor digital compliance and corporate stewardship.

Can I use a generic template for my PAIA manual?

Whilst you can start with the official 2021 template provided by the Information Regulator, it must be meticulously customised to reflect your specific business operations. A generic document that doesn't accurately list your record categories won't satisfy a compliance assessment. We incorporate this customisation into our 5-stage development process, ensuring your documentation is both legally sound and professionally presented within your site's unique architecture to foster trust with your audience.

What are the fees associated with a PAIA request in 2026?

Requesters are typically required to pay a standard request fee when submitting Form 2, followed by an access fee if the request is granted. These fees are determined by the Information Regulator and cover the costs of searching for and preparing the requested records. You must clearly state these fees in your manual to maintain transparency. Ensure your manual reflects the current ZAR fee schedules to avoid disputes during the request process.

Does the Information Regulator check websites for PAIA compliance?

Yes, the Information Regulator has significantly strengthened its oversight and now conducts regular compliance assessments, which include reviewing company websites for accessibility. Failure to publish a compliant paia manual for website south africa can trigger a formal investigation or physical inspection of your records. Proactive digital compliance is essential to avoid administrative fines and protect your corporate reputation in an era of increased regulatory transparency and active enforcement.

Who should be appointed as the Information Officer for my company?

By default, the head of a private body, such as the Managing Director or CEO, is the designated Information Officer. However, you can officially delegate these responsibilities to a Deputy Information Officer who possesses the technical knowledge to manage requests. This person must be registered through the Regulator’s eServices portal. Appointing a meticulous individual ensures that your organisation handles information requests with the strategic depth and reliability required by South African law.